

A secret, nationwide operation has secured tens of thousands of UK fridges and freezers from hackers, the BBC reported on 20 November 2026, after researchers found a weakness in refrigeration controllers used by supermarkets, warehouses, restaurants and stadiums across Britain.
The UK fridge hack that never happened was, by all accounts, a close-run thing. Security researchers flagged the flaw in late October, and industry, the National Cyber Security Centre (NCSC) and government departments then raced to close it before criminals or state-backed hackers could find it.
What was the UK fridge hack risk?
Three waves of attacks on refrigeration temperature controllers have already hit this year, according to the BBC. In August, fridges at a small number of US military bases were affected. On 11 and 12 October, hundreds of supermarkets and food-processing sites in France were hit when Danfoss temperature control systems were targeted. On 1 and 2 November, dozens of supermarkets across seven European countries were hit, with Belgium and Luxembourg the worst affected, and a small number of French blood bank sites were also disrupted.
The damage abroad has been serious: tonnes of food spoiled at hundreds of stores and millions of pounds of losses. France has blamed Iran for one wave of attacks on its supermarkets, a claim Tehran denies. Britain was thought to have largely escaped because its refrigeration trade relies on different devices.
How was the flaw found?
It was not quite that simple. Staff at refrigeration consultants Omega Solutions examined the most popular controllers in the UK, made by British firm Resource Data Management (RDM), after the European attacks. Their findings were verified and expanded by experts at Pen Test Partners.
“These popular controllers had a similar weak password problem to the Danfoss and other controllers that were attacked so successfully in previous hacks so we had to get the message out as soon as possible and keep it secret,” said Ken Munro of Pen Test Partners. He added that it was likely only a matter of days before criminals or nation-state hackers worked it out.
RDM disputes how critical the vulnerabilities are. Chief executive Ged Evans said the weakness was identified in a test environment that “went beyond” usual exercises because it involved dismantling the firm’s hardware. The ethical hackers counter that such hardware can be bought cheaply on sites such as eBay. RDM says it has already released first patches, has contacted customers and has seen no sign of malicious activity on its controllers.
How were the fridges secured?
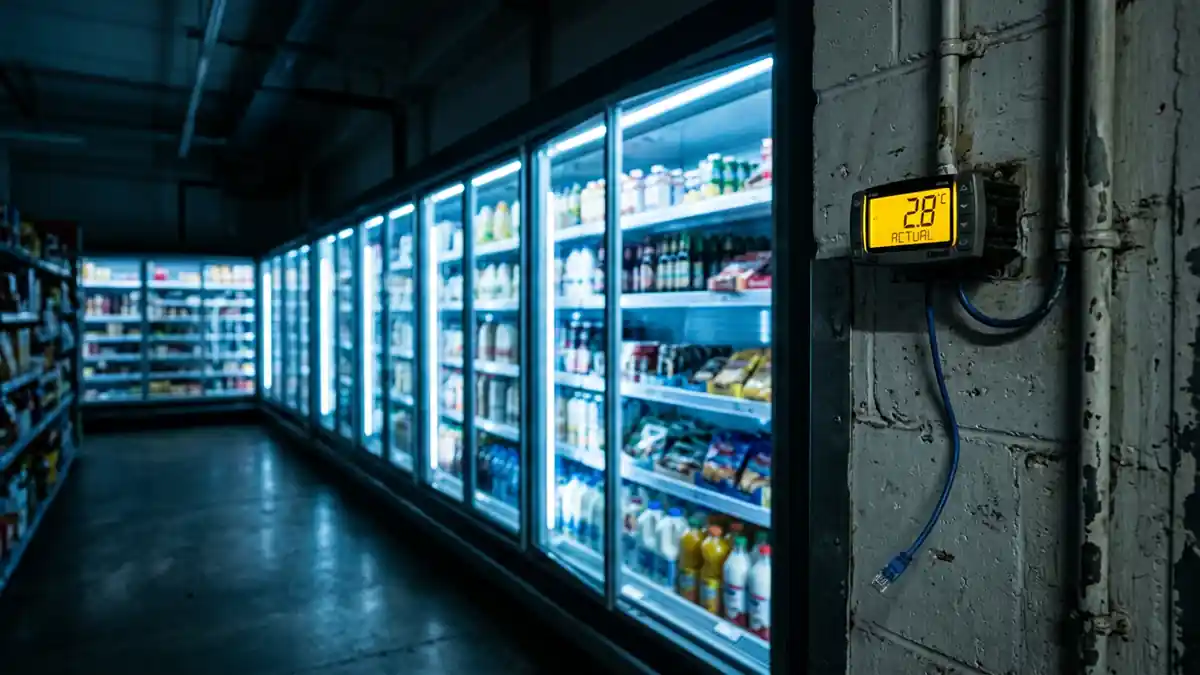
The NCSC, the Department for Environment, Food and Rural Affairs and the Food Standards Agency joined industry conference calls and tasked teams to contact firms at risk. Thousands of devices, each able to control dozens of fridges and freezers, were taken off the open internet, some remotely and some physically, with staff told to pull network cables and check temperatures by hand.
The BBC understands most major supermarkets had to divert IT teams. One worker at a large chain, who was not named, said hundreds of devices were taken offline every day for a week. “It did feel like a race against time as we were expecting another wave of these fridge hacks to come,” they said, warning that warehouses holding millions of pounds of food could have been ruined.
The warning also went out to convenience stores, petrol stations, restaurants and fast-food chains, sports arenas, hotels, food-processing plants and cold-storage sites. The BBC held off reporting the story until now so as not to tip off attackers.
What it means for you
For shoppers, there is nothing to do: no UK food spoilage has been reported, and the BBC says there was no sign of malicious activity on the controllers. The episode does explain why some staff were quietly checking fridge temperatures by hand in recent weeks.
For business owners, the lesson is practical. If you run refrigeration controllers connected to the internet, change default or weak passwords, remove them from the open internet where you can, apply manufacturer patches and keep a manual temperature-check routine as a fallback. The NCSC publishes guidance for organisations on basic cyber hygiene.
What happens next
The vulnerability may be contained, but the wider picture is unsettled. This is the latest in a run of cyber stories on this site, including the AI-discovered Java4Shell flaw in Java, and the BBC has separately asked why so many tech outages are happening, noting there is no evidence they are linked. Expect more scrutiny of the internet-connected kit hidden in the back rooms of shops and warehouses. For more, see our tech coverage.